build · August 2026
Spec-Driven Development: the control plane for AI-native software engineering
Coding agents make implementation cheaper, not correctness automatic. A practical guide to using specifications, repository evidence, verification, and human decision gates to coordinate agentic software delivery.
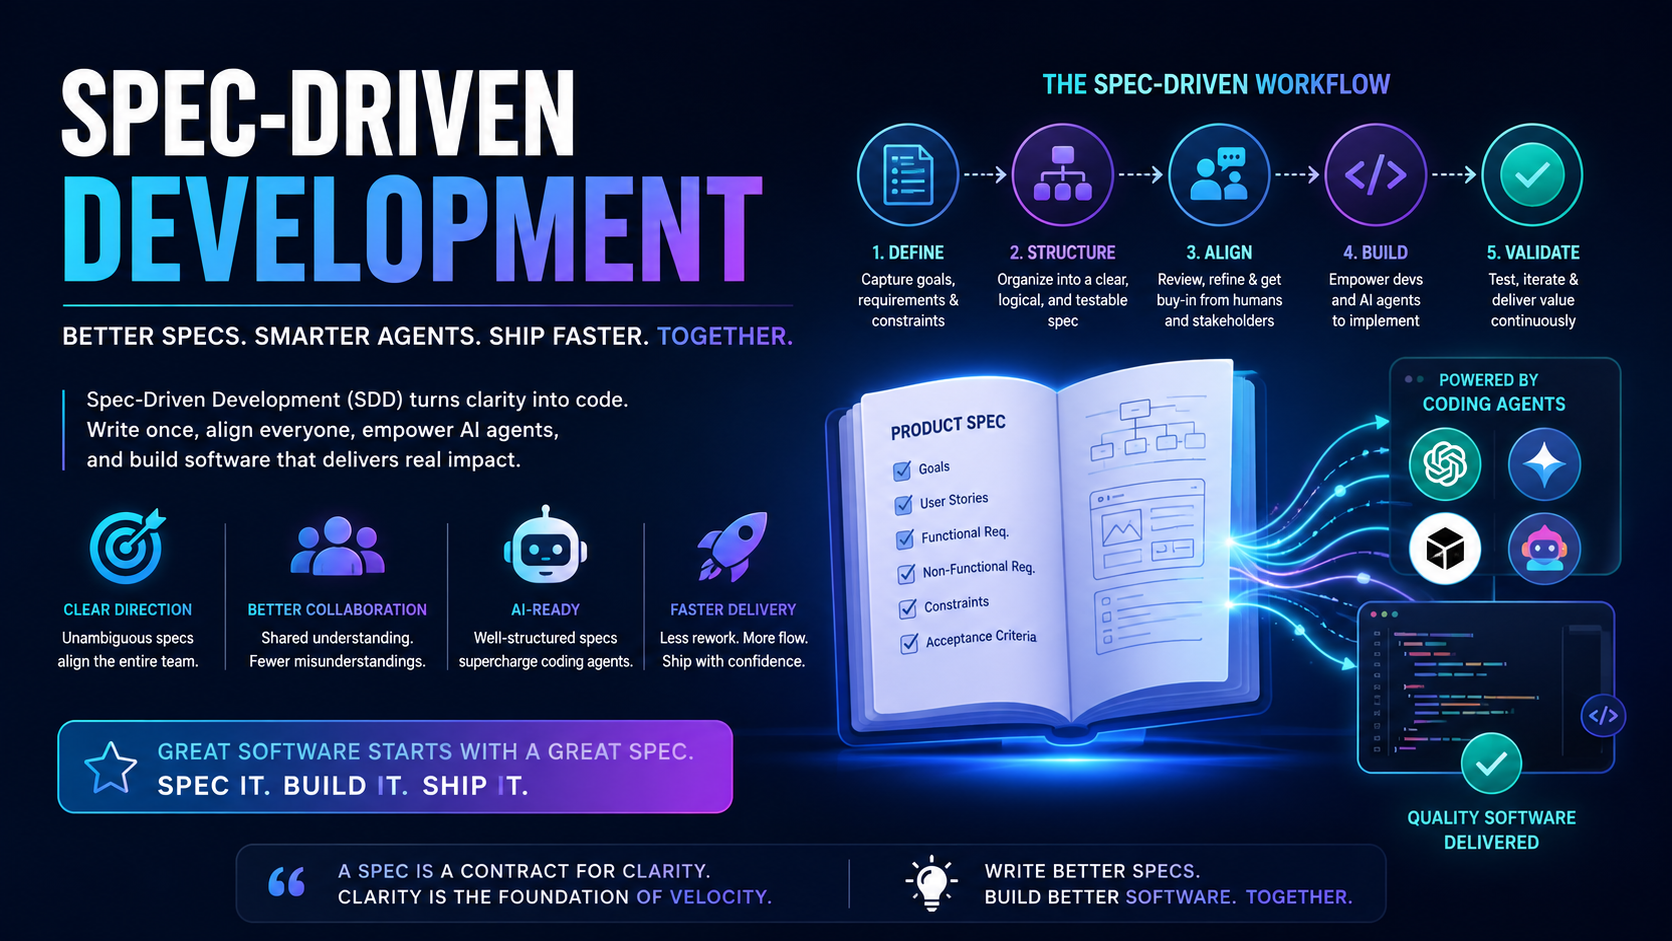
A coding agent can turn a short request into a surprising amount of code: APIs, schemas, migrations, tests, documentation, and a pull request. The useful question is no longer only can we implement this? It is increasingly do we agree on the intended behavior, constraints, and evidence of correctness?
This is the promise of Spec-Driven Development (SDD): not documentation for documentation’s sake, and not a return to frozen requirements. It is a way to make intent explicit, reviewable, versioned, and increasingly machine-actionable—so humans and coding agents can work against the same contract.
The shift: from code-centric to intent-centric delivery
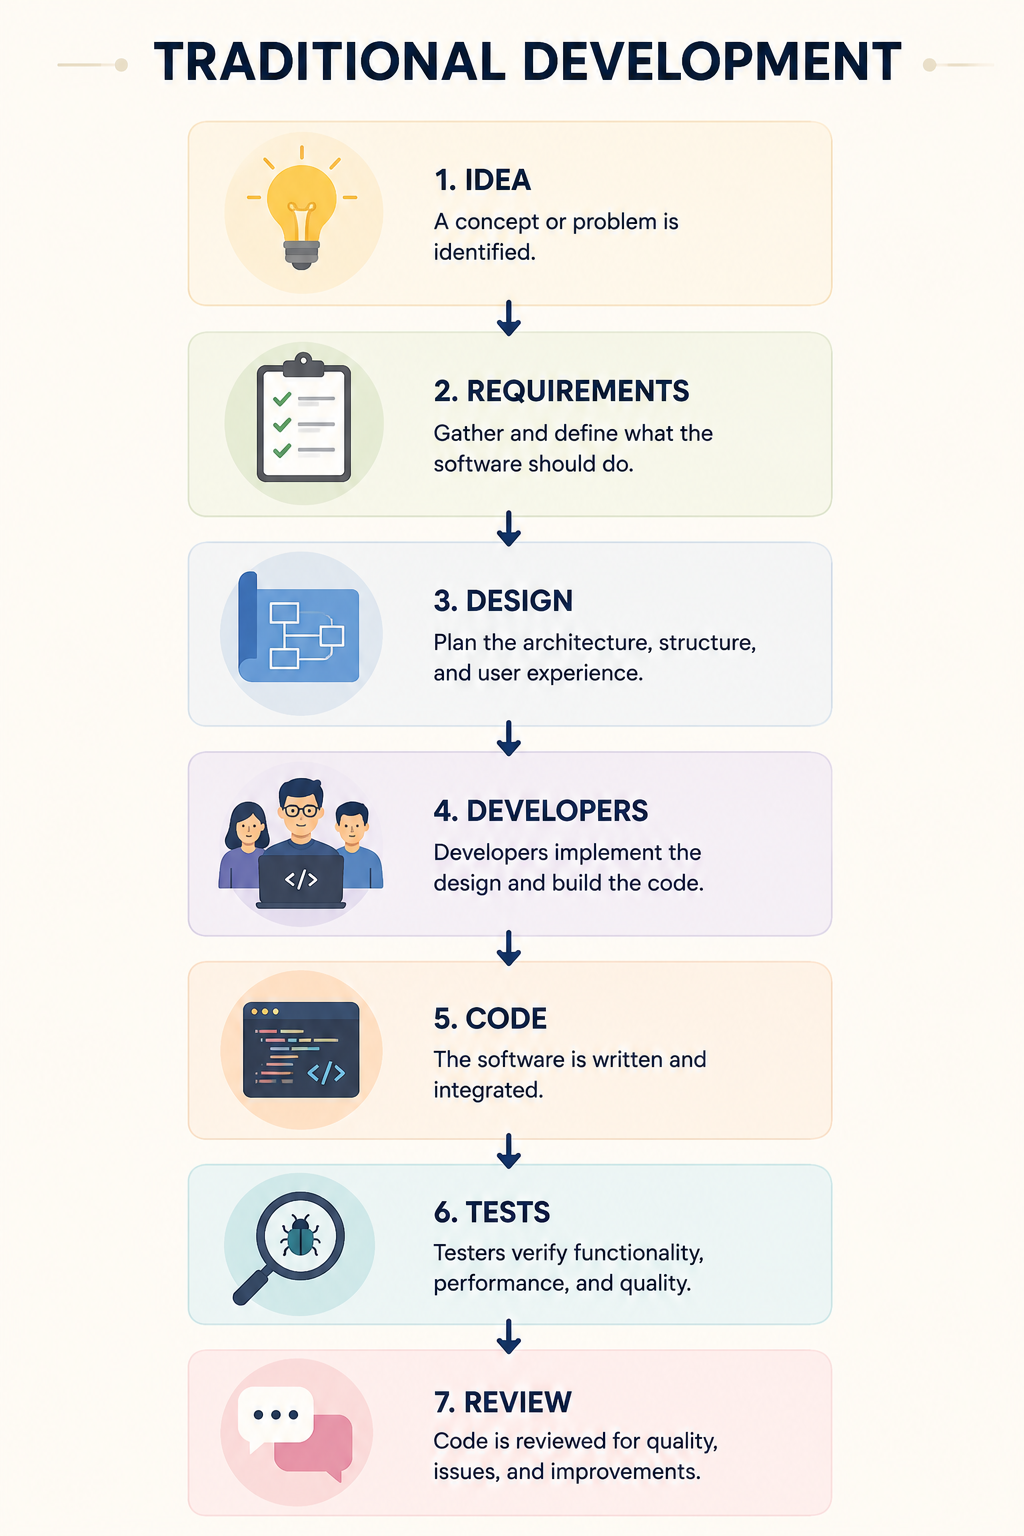
Traditional engineering already had specifications: product requirements, design documents, API contracts, acceptance criteria, tests, and architecture decisions. The novelty is economic. When writing code was the expensive part, incomplete intent could sometimes be resolved through the slow, conversational work of implementation. When agents can produce a large implementation quickly, ambiguity scales into review load, duplicate abstractions, unsafe assumptions, and costly rework just as quickly.
| Practice | Primary question | How SDD relates |
|---|---|---|
| PRD / user story | Why does this matter and for whom? | Supplies the product intent that a feature spec sharpens. |
| Requirements engineering | What behavior and constraints are required? | SDD operationalizes requirements as versioned artifacts for humans and agents. |
| TDD | What executable behavior should fail before code exists? | Tests provide implementation-level evidence; they do not replace product and architecture intent. |
| BDD | What observable examples create shared understanding? | Scenarios can become a testable part of the specification. |
| API / contract / policy as code | Which interfaces and rules are enforceable? | These are high-value, machine-checkable parts of a broader specification. |
| Architecture decision record | Why did we choose this consequential path? | ADRs preserve decisions that constrain future agent work. |
The ideas are old. The economics are new.
SDD should not be presented as if software teams suddenly discovered requirements. It sits on a long line of practices: requirements engineering, design by contract, TDD, BDD, executable specifications, infrastructure as code, policy as code, and versioned architecture decisions. The new capability is that an agent can consume these artifacts directly and act on them. The new risk is that it can also act on a vague or wrong artifact at high speed.
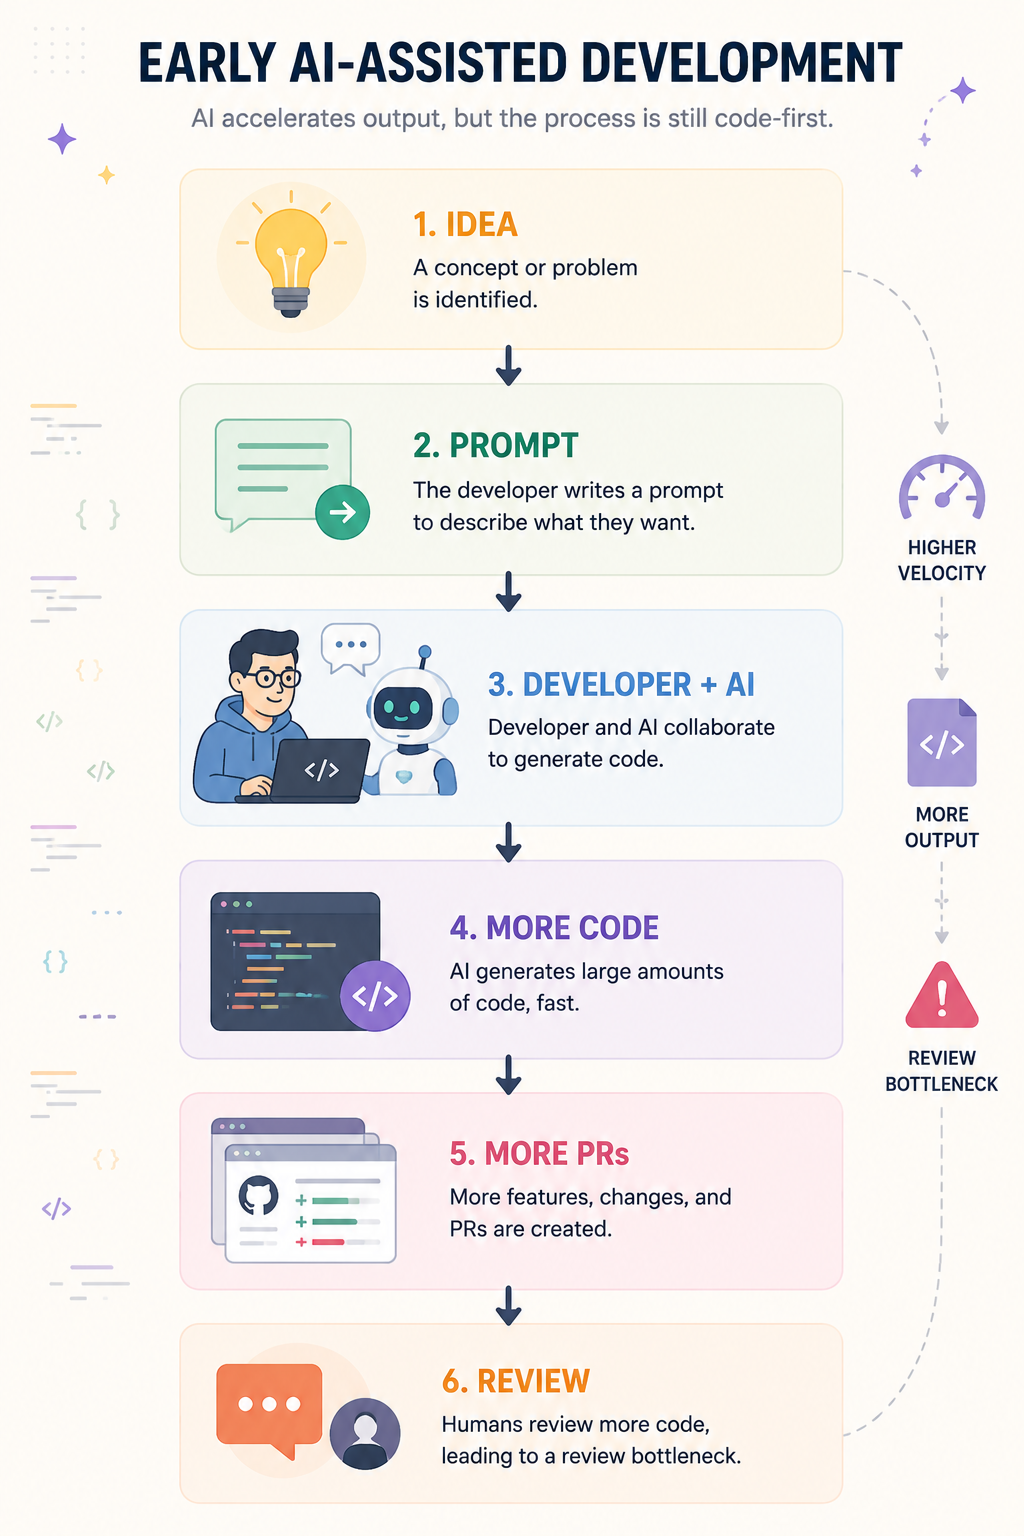
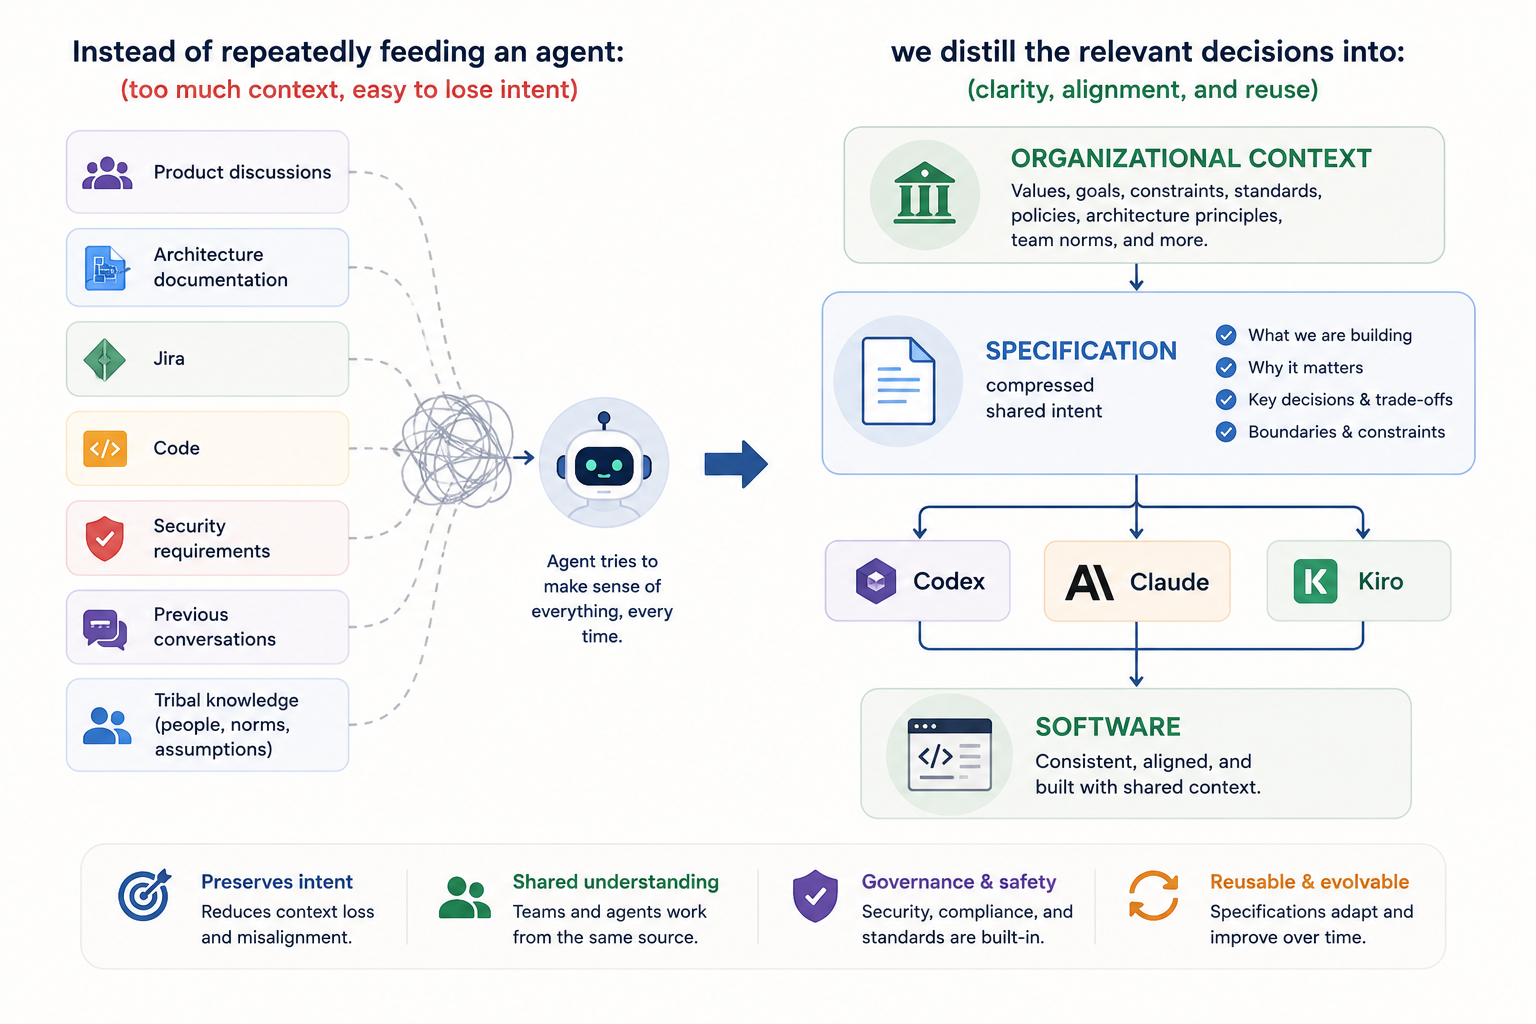
The practical response is not to make every prompt longer. It is to make the decisions that shape a change explicit, reusable, and reviewable before agents multiply the implementation work.
Specifications as the intent layer
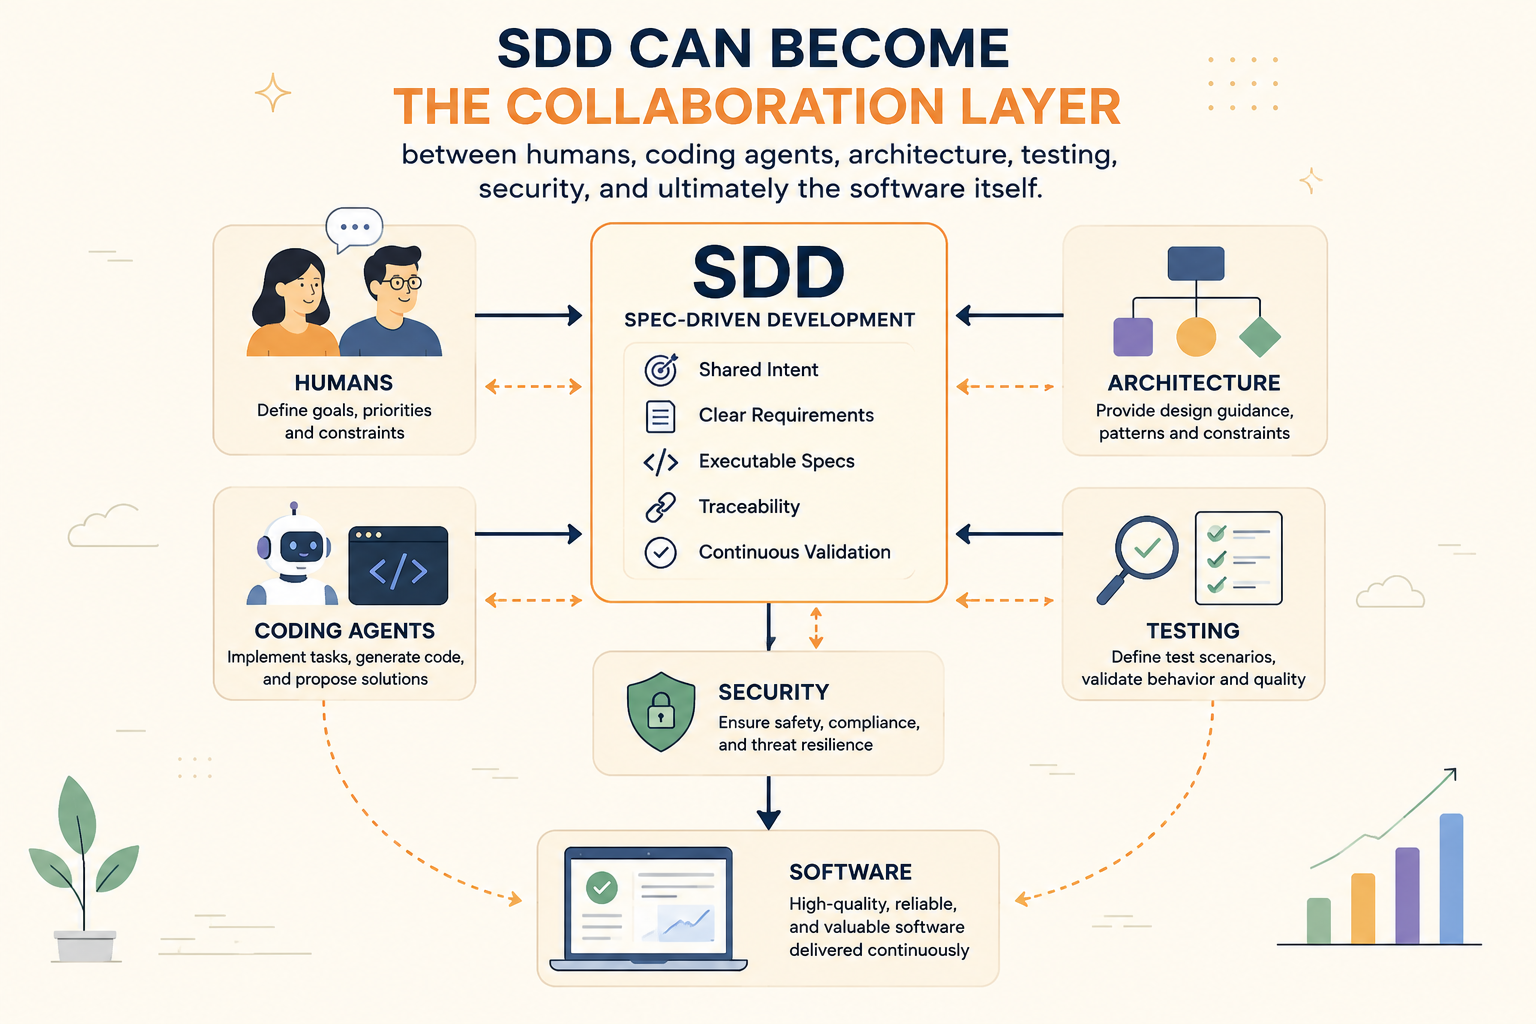
In an AI-native delivery system, the specification can become an explicit layer between human and business intent, technical planning, agent execution, code, and runtime evidence. It records what must be true, what must not change, who decides, and how the team will know the change worked. Code remains the executable implementation; the spec is the contract used to judge whether that implementation belongs.
SDD is context engineering—not context replacement
A serious coding task may depend on repository structure, Git history, API contracts, prior decisions, security policy, tests, operational practices, and product context. Dumping all of that into an agent context window is neither efficient nor reliable. A good specification is a curated compression of intent: it routes the relevant facts, constraints, scenarios, and evidence expectations to the task at hand.
But a specification cannot replace repository grounding. For brownfield work, an agent should inspect the actual codebase before proposing design. Otherwise it can invent a clean-sounding abstraction that duplicates an existing session service, cache repository, contract, or test harness.
Repository-grounded SDD: a practical workflow
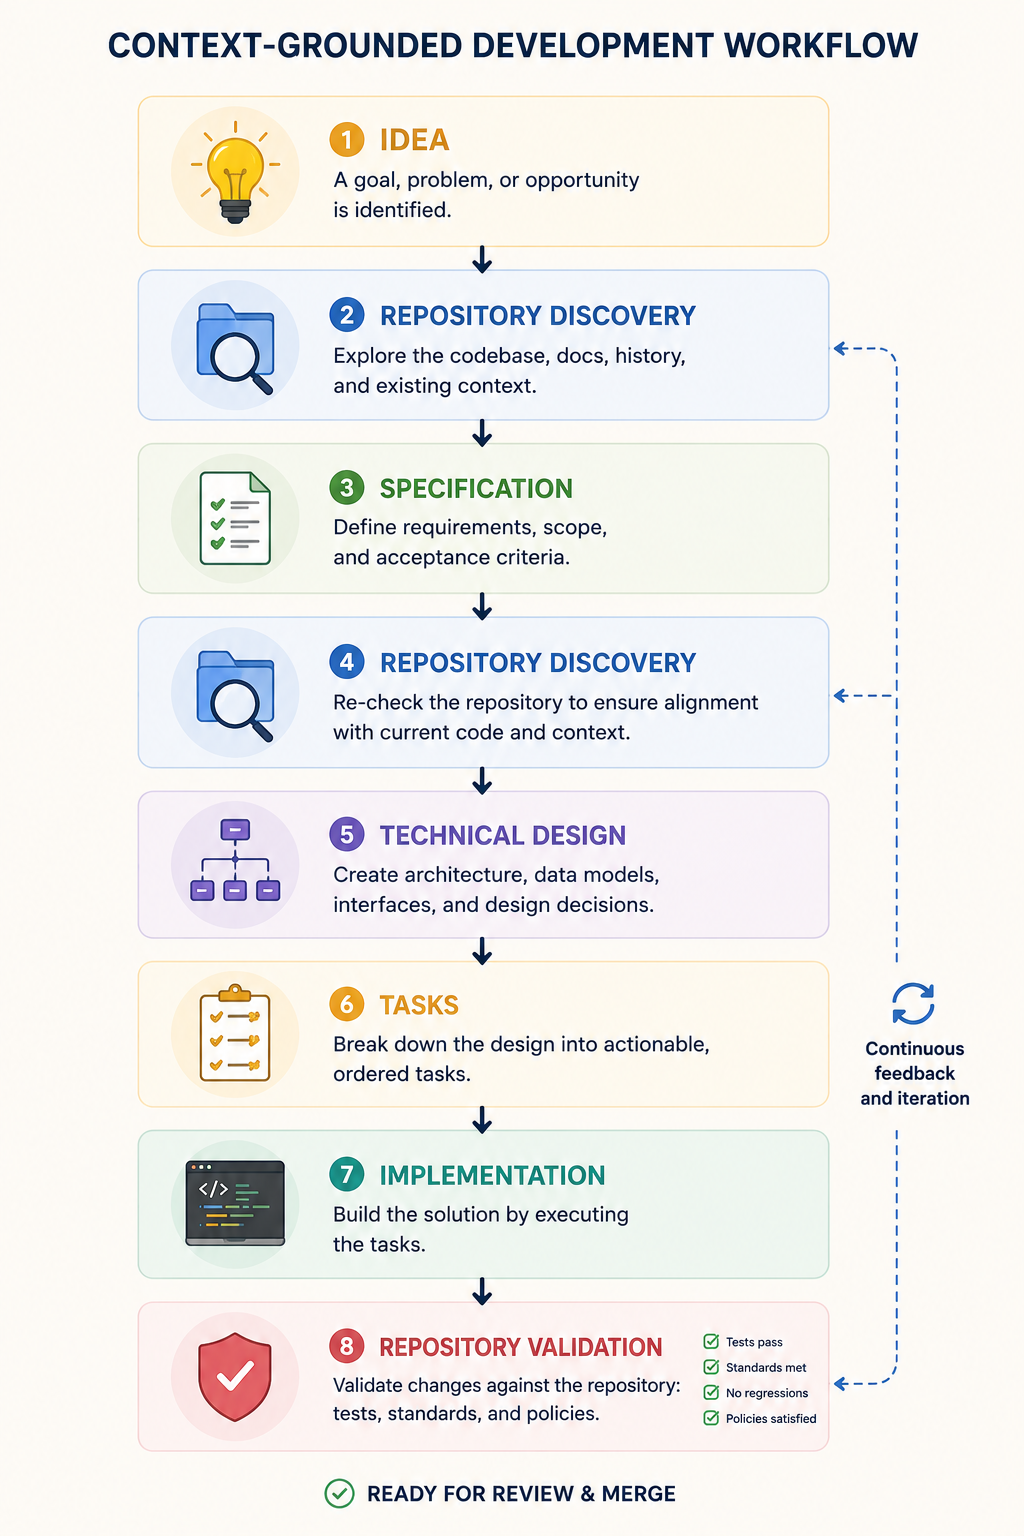
The key addition is reconnaissance before design. A technical plan should cite the actual evidence it relies on. That makes an agent’s proposal reviewable and gives a future maintainer a path back to the surrounding system—not merely a generated explanation.
## Repository evidence

Existing implementation: src/auth/session.py
Existing abstraction: src/cache/redis_session_repository.py
Existing API contract: contracts/auth.yaml
Existing tests: tests/auth/test_session.py
Relevant decision: docs/adr/ADR-014-session-storage.md

Design constraint: extend the existing session path; do not create a parallel token service.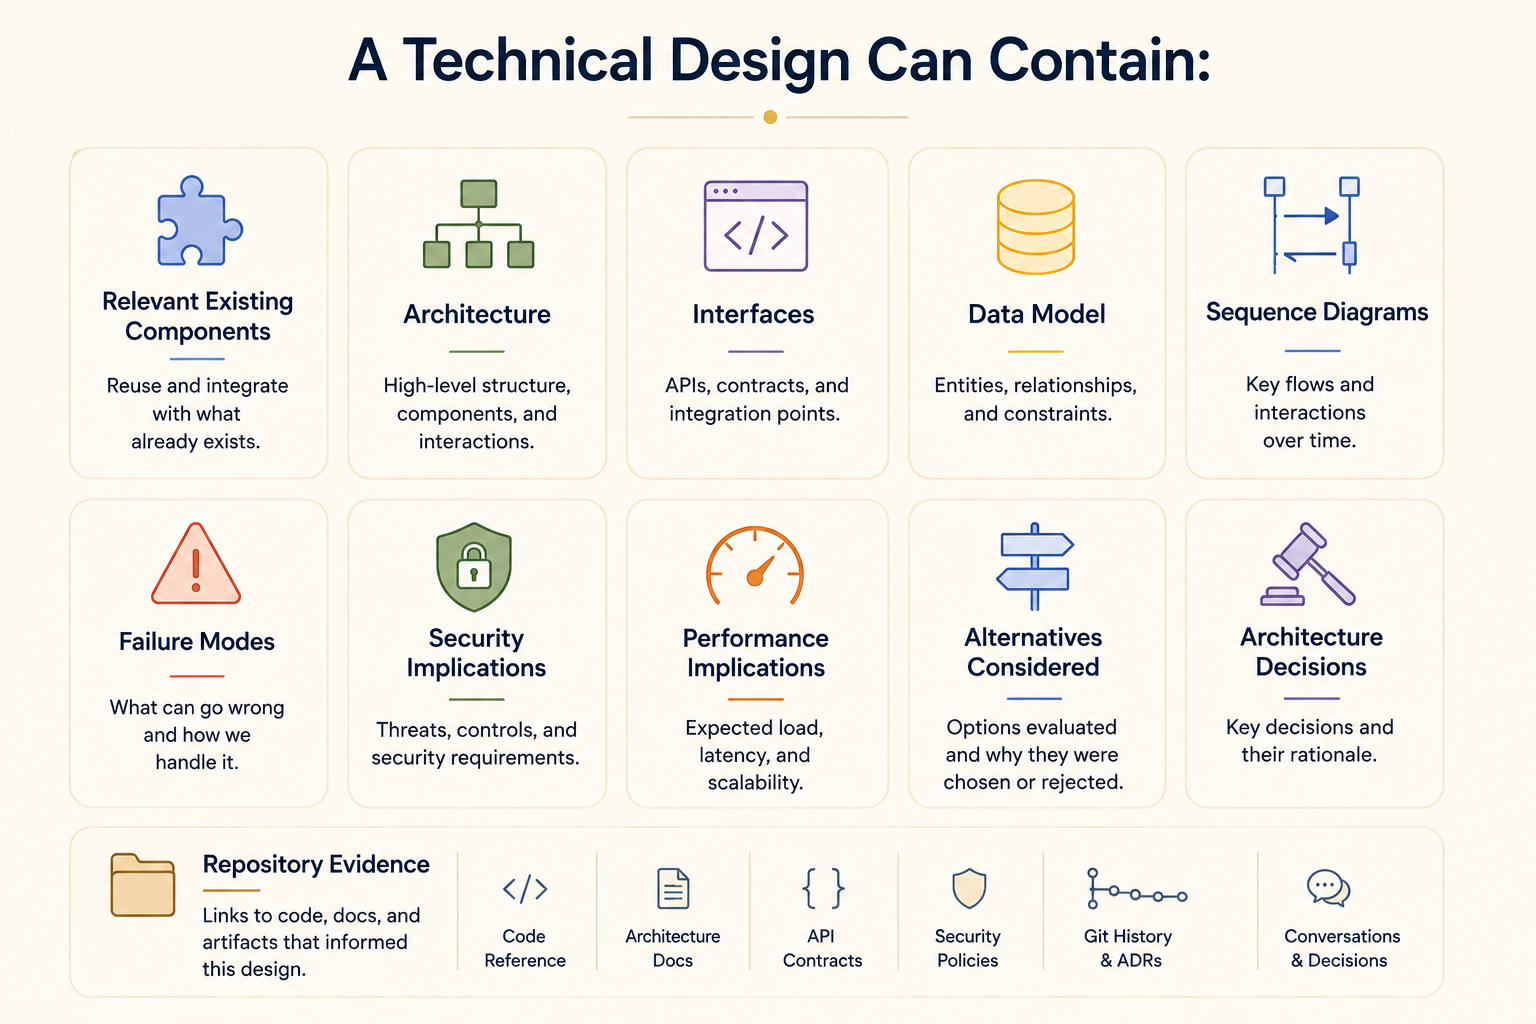
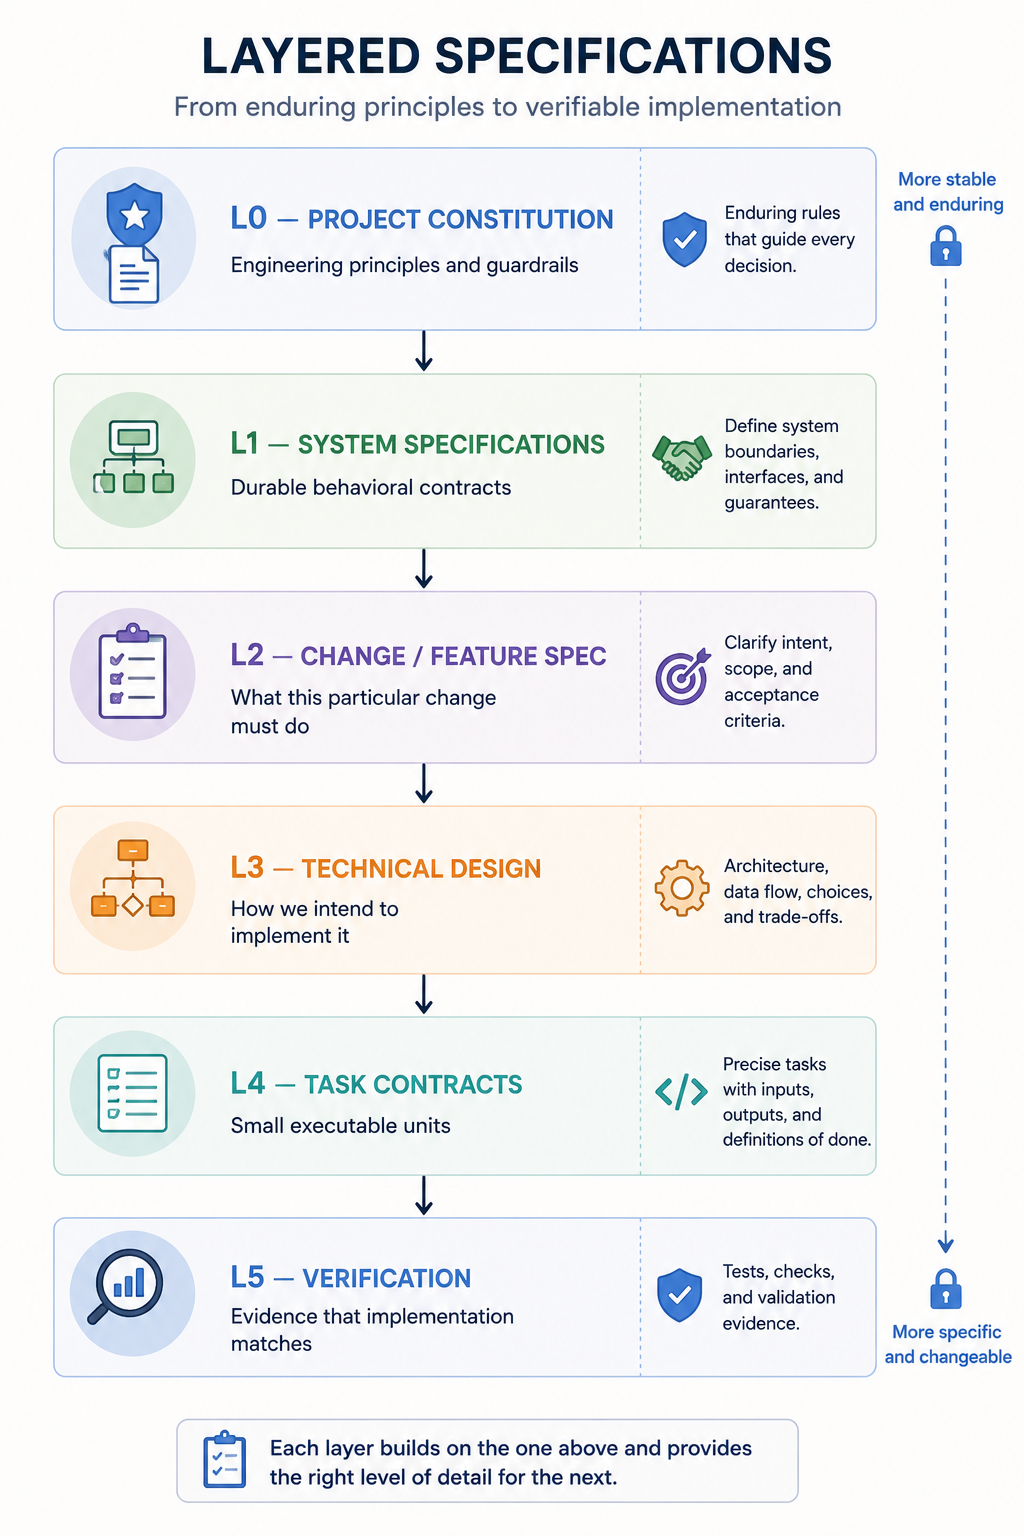
A layered artifact stack avoids one enormous spec
The answer is not a 100-page document for every change. Mature SDD separates durable principles from change-specific work, and separates behavior from implementation detail. Each layer has a different owner, lifetime, and review burden.
Make requirements testable: EARS plus scenarios
Kiro’s current Requirements-First workflow uses EARS-style requirements—typically WHEN condition, THE SYSTEM SHALL behavior—then derives design and tasks. That format is useful because it makes a hidden ambiguity visible. BDD complements it with observable GIVEN / WHEN / THEN examples. Neither notation guarantees that the underlying decision is right; both make it easier to challenge and verify.
AUTH-001 — idle session expiration

WHEN an authenticated session has been inactive for more than 30 minutes
THE SYSTEM SHALL reject the next authenticated request
AND require re-authentication.

Scenario: expired session
GIVEN an authenticated session with no activity for 30 minutes
WHEN the user makes another authenticated request
THEN the response is unauthorized
AND no protected resource is returned.
The requirement says what and why. The design decides how: where last activity is stored, how concurrent tabs behave, whether a long-running request extends activity, how a distributed store handles failure, what is logged, and which compatibility boundaries apply. Keeping these separate lets the behavior remain stable while implementation evolves.
From vague ticket to task contract
“Add automatic session timeout” is not an agent-ready task. It says nothing about the duration, activity definition, concurrent sessions, store failure, public APIs, migration behavior, security expectations, or proof of success. A bounded task contract puts the agent inside an explicit architecture envelope.
Task T-04 — implement idle-session expiration

Objective: satisfy AUTH-001 and AUTH-003.
Relevant components: src/auth/session.py, src/api/middleware.py
Do: extend the existing RedisSessionRepository; emit session_expired telemetry.
Do not: introduce a new token format or change public auth responses.
Verification: pytest tests/auth/test_session_timeout.py; contract test auth.yaml
Definition of done: requirements mapped, tests passing, telemetry documented.
Traceability is how intent survives high-speed change
A stable requirement ID is not bureaucracy when it lets a reviewer travel from a behavior to its design, task, implementation, test, pull request, and operational signal. This is especially valuable with agents: generated code can be abundant, but it should not be difficult to answer which requirement authorized it or which evidence supports it.
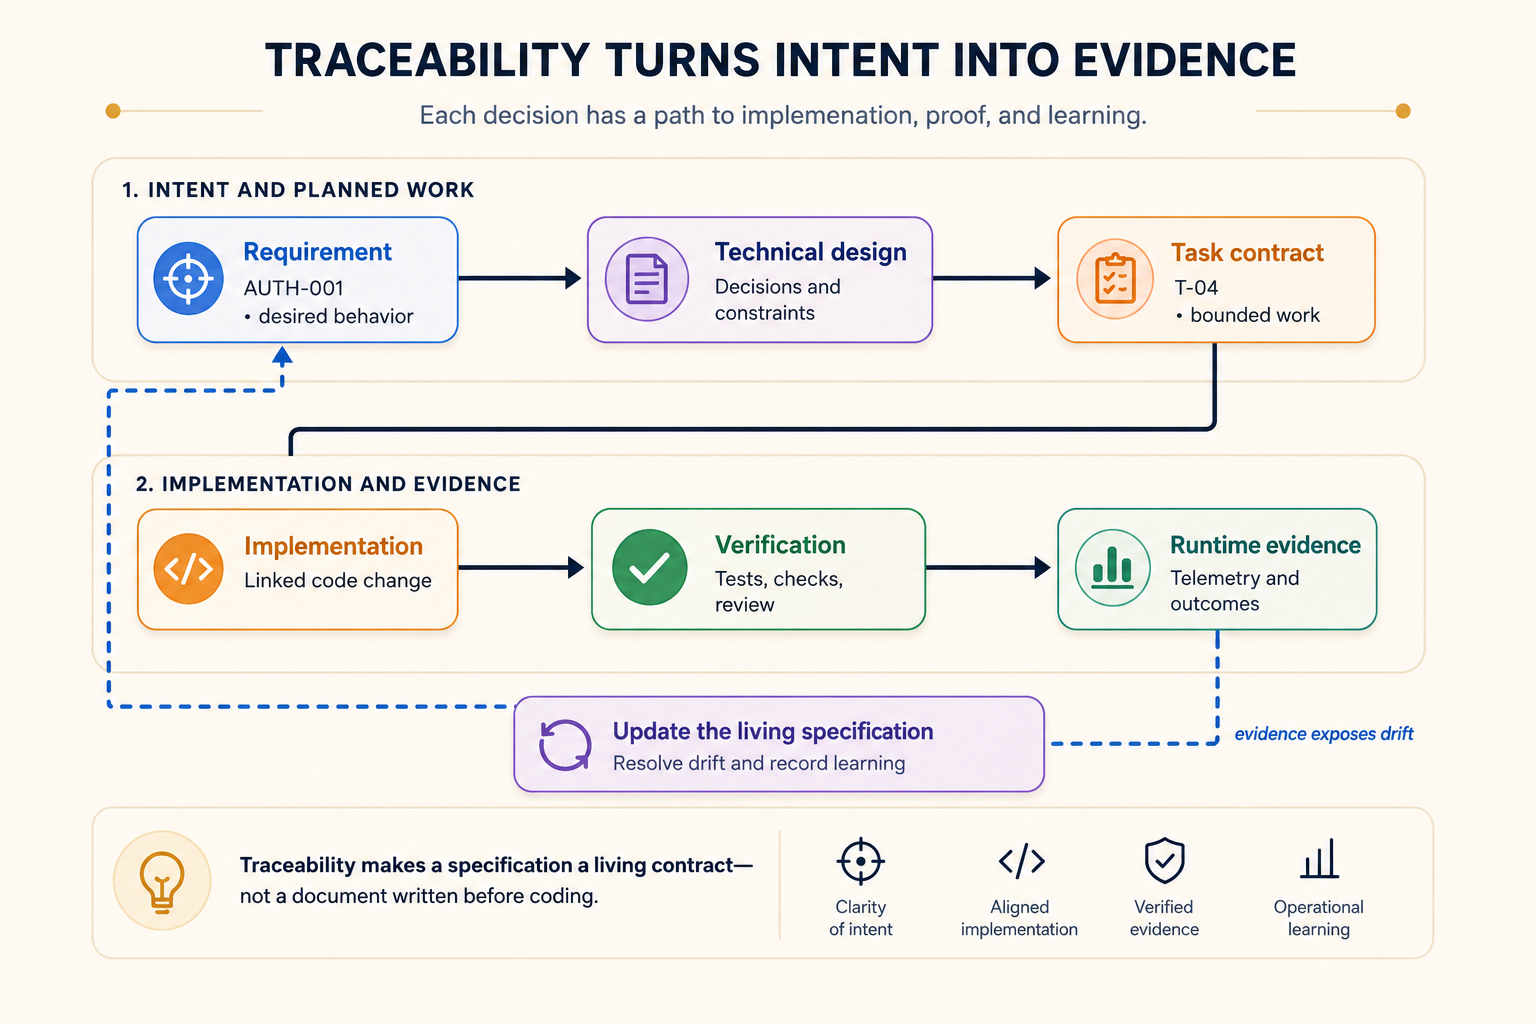
| Requirement | Design | Task | Implementation | Evidence | Status |
|---|---|---|---|---|---|
| AUTH-001 | §4.2 | T-04 | session middleware | idle-timeout test + auth events | PASS |
| AUTH-002 | §4.3 | T-05 | refresh path | refresh test | PASS |
| PERF-001 | §7 | T-09 | middleware | benchmark + p95 telemetry | PARTIAL |
| SEC-001 | §6 | T-08 | session store | threat review | MISSING |
A matrix like this makes useful questions cheap: Which requirements have no test? Which changed after implementation started? Which code changed without a linked behavioral reason? The table is not proof by itself; it is a map for targeted review and automation.
Specification drift is the operating problem
SDD fails if the spec becomes a static artifact. Bug fixes, emergency changes, refactors, and operational learning can all make SPEC ≠ REALITY. Treat the loop as part of delivery: a behavior-changing pull request updates the relevant spec or records why it is intentionally unchanged; tests and runtime evidence expose gaps; the accepted current spec becomes the next task’s grounding.
- Use change proposals or delta specs for non-trivial changes.
- Make spec references and verification evidence visible in pull requests.
- Add contract and architecture checks where they are deterministic.
- Use independent agent analysis as a review aid, not as an unquestioned gate.
- Archive completed changes into the canonical behavior model so future work starts from current truth.
What today’s SDD tools teach us
GitHub Spec Kit, OpenSpec, and Kiro are useful examples of an emerging tool category—not interchangeable products and not evidence that one rigid workflow fits every team. Their important contribution is architectural: they make intent, plans, tasks, and change lifecycle artifacts first-class inputs to agent work.
| Dimension | GitHub Spec Kit | OpenSpec | Kiro |
|---|---|---|---|
| Core model | Spec → plan → tasks → implement, with a constitution and analysis/convergence steps. | Canonical current specs plus change folders containing proposal, delta specs, design, tasks, and archive lifecycle. | Requirements, design, and tasks as an integrated agent workflow; requirements-first, design-first, and quick variants. |
| Strength for agents | Agent-portable Markdown workflow and cross-artifact consistency checks. | Makes the behavioral diff explicit—a strong fit for brownfield change management. | Guided requirements, EARS-style acceptance criteria, task execution, and review checkpoints. |
| Trade-off | Teams must tailor templates and governance to their repository. | Requires discipline around syncing and archiving changes. | Workflow lives in a product environment; teams should preserve portable artifacts where possible. |
| Practical lesson | Separate principles, intent, plan, and implementation. | Maintain a current truth and explicit deltas. | Make requirements, design, tasks, and review gates easy to use. |
Tool independence matters
Do not make one agent the sole holder of organizational intent. Markdown in Git, OpenAPI, JSON Schema, ADRs, test artifacts, and policy files are portable across Codex, Claude Code, Copilot, Kiro, and future tools. An agent should consume and improve the evidence; it should not trap the only version of the team’s reasoning in a proprietary chat history.
Human decision gates and independent verification
The right operating model is not “human writes every line” versus “agent does everything.” Humans provide the most leverage where ambiguity, irreversibility, values, and trade-offs are highest: approve intent, resolve genuine ambiguity, choose consequential architecture, define risk tolerance, and accept exceptions. Agents are excellent at structuring a draft, searching repository evidence, decomposing work, implementing bounded tasks, and assembling verification evidence.
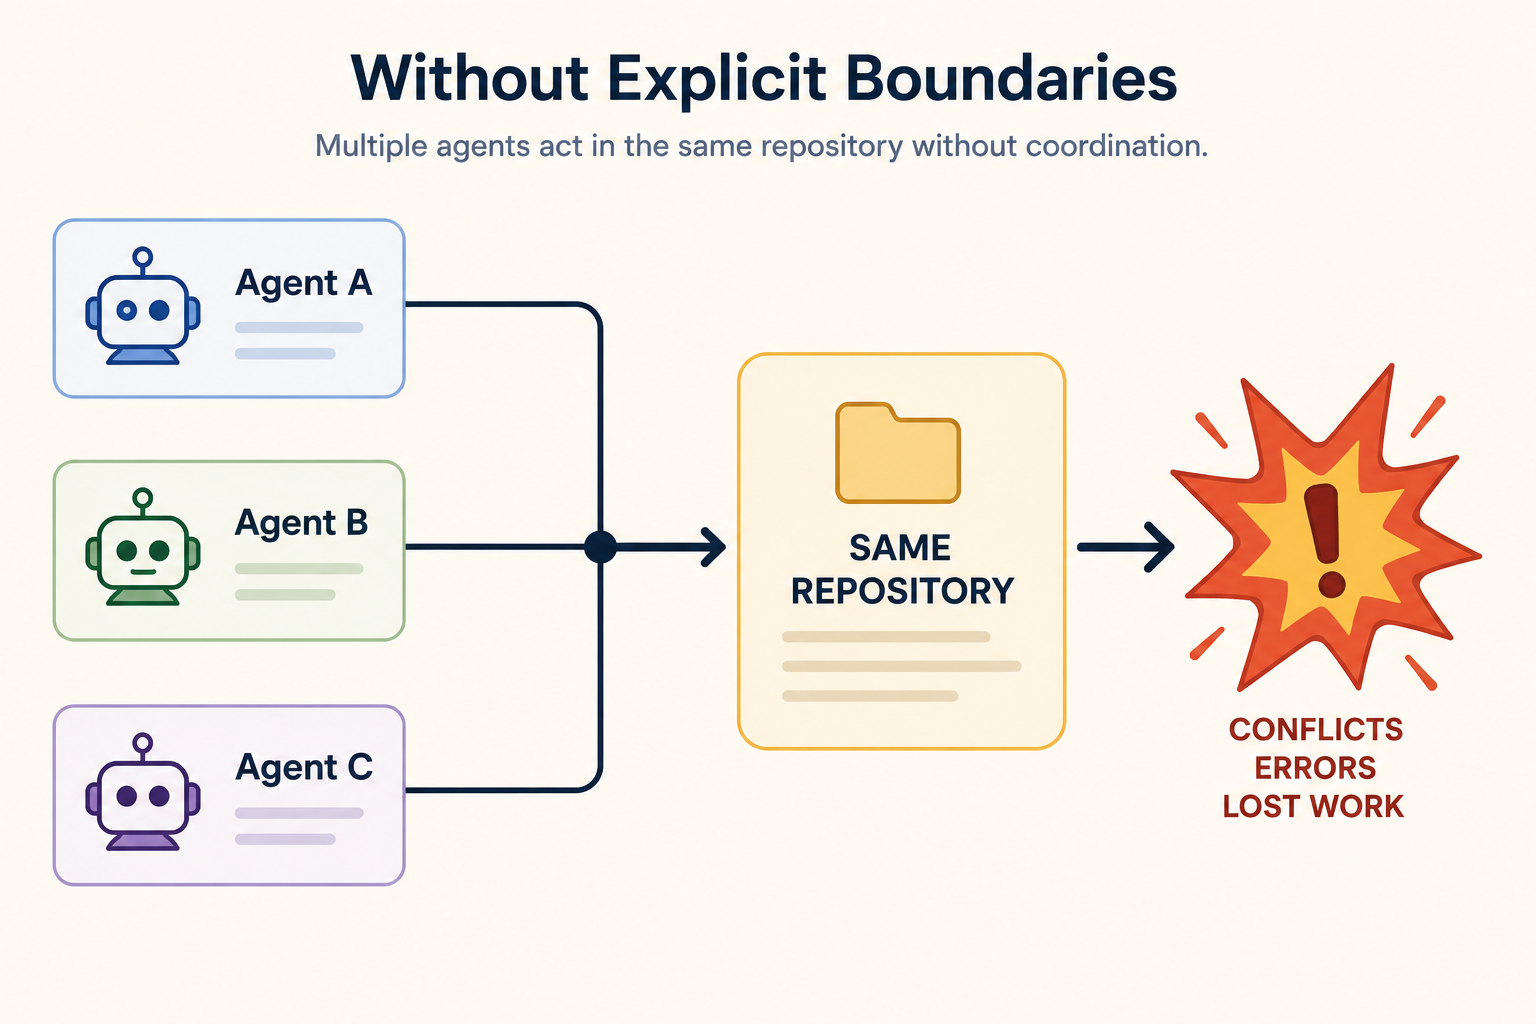
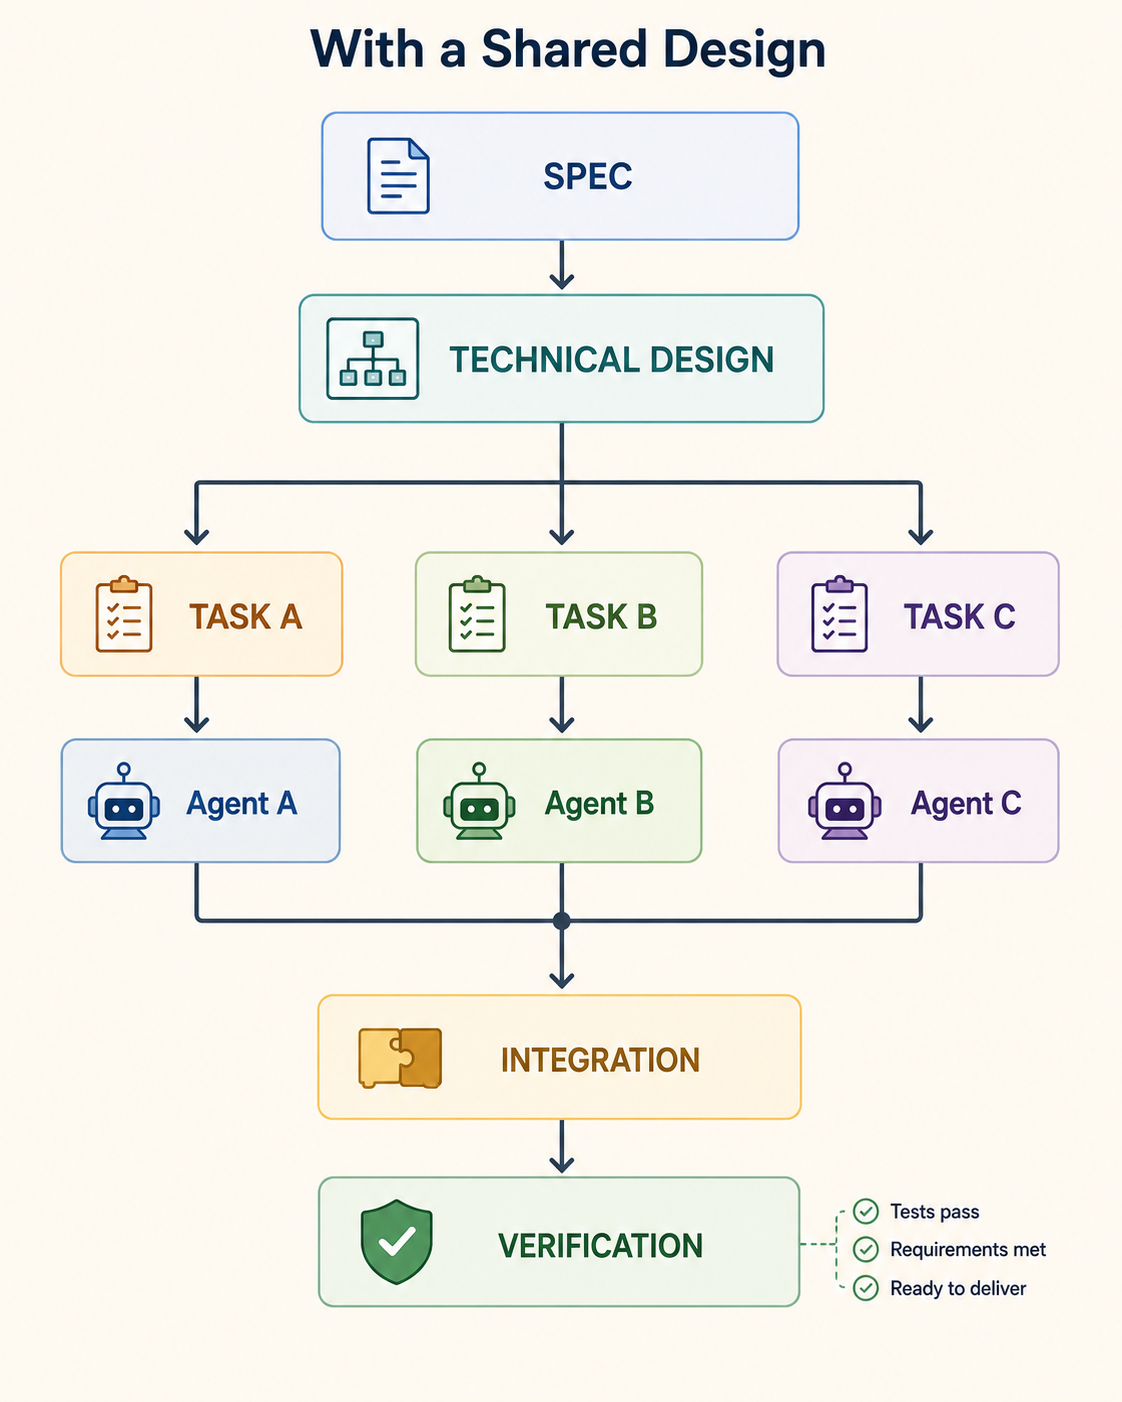
For multi-agent work, the specification becomes even more important. A shared design contract and task graph can assign ownership boundaries—API contract, persistence, frontend, integration tests—while preventing four agents from making four incompatible assumptions. Parallelism without contracts simply moves merge conflicts and review debt downstream.
| Activity | Primary role | Why |
|---|---|---|
| Problem framing and success criteria | Human accountable, agent assists | Business value and acceptable trade-offs cannot be inferred reliably from code. |
| Repository reconnaissance | Agent investigates, human challenges | Agents can cover breadth; humans validate the interpretation and consequential assumptions. |
| Architecture decisions | Human approves, agent proposes | Architecture changes create long-lived coupling and operational obligations. |
| Bounded implementation | Agent leads with human oversight | This is where structured context and automated checks compound speed. |
| Spec compliance and testing | Independent verifier plus deterministic CI | The builder should not be the only judge of its own work. |
| Acceptance and risk exceptions | Human accountable | Acceptance is a governance decision, not simply a passing build. |
SDD does not replace Agile—it can prevent agentic Waterfall 2.0
Bad SDD writes a massive spec, freezes it, and implements for months while reality changes. Good SDD uses progressive rigor: discover enough intent to make the next safe decision, prototype or validate, update the living spec, and continue in small reviewable batches. The artifact set should grow with risk, not with a team’s appetite for paperwork.
| Change profile | Appropriate rigor | Typical artifacts |
|---|---|---|
| Low risk, local, reversible | Spec first | Outcome, boundary, test or acceptance example. |
| Production feature or API | Spec anchored | Requirements, design, task contracts, tests, PR evidence. |
| Cross-service, security, data migration | Structured SDD | Change spec, ADR, threat analysis, rollout and rollback, traceability. |
| Regulated or high-consequence system | Governed SDD | Named approvals, controls, traceability, independent verification, runtime evidence. |
Where Spec-Driven Development can go wrong
- Specification theater: documents exist but no planning, review, or CI decision actually uses them.
- AI-generated spec bloat: a model creates hundreds of requirements that no accountable human can inspect.
- False precision: a well-formatted requirement can encode a bad product assumption.
- Context blindness: the spec ignores repository evidence and the agent invents parallel abstractions.
- Architecture by agent: humans approve fluent generated designs without understanding consequences.
- Confirmation bias: the same agent drafts the spec, implementation, and verdict without independent challenge.
- Tool lock-in: intent survives only in one vendor’s chat or workspace.
- Metrics gaming: traceability coverage becomes the goal instead of useful behavior and operational quality.
Spec debt is intent uncertainty
Technical debt is accumulated implementation compromise. Spec debt is accumulated uncertainty about intent: undocumented behavior, contradictory requirements, stale decisions, tests with no known behavioral reason, or a capability with no clear owner. Agentic delivery can amplify both. A fast agent can add code to an already ambiguous system faster than a team can recover the reasoning behind it.
A realistic CI/CD future: deterministic checks first, probabilistic checks second
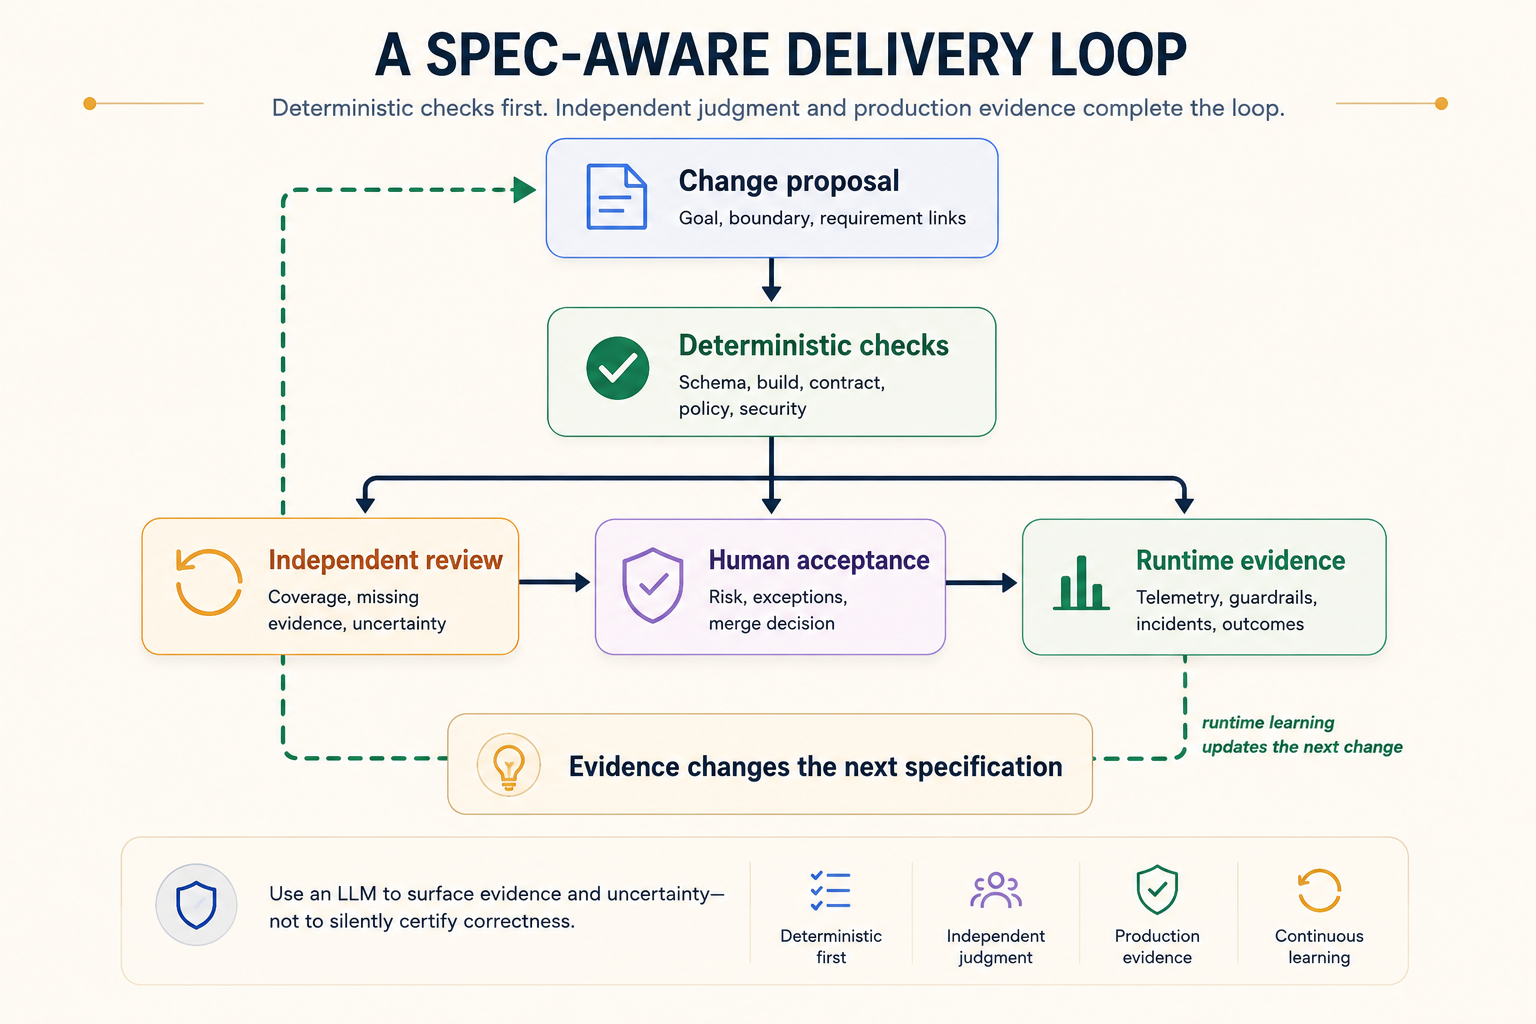
Some specification governance is practical today: enforce file structure, require a linked requirement ID for behavior-changing changes, validate schemas, run contract tests, lint policy, execute security checks, and verify coverage reports. Other checks—whether code “really” fulfills an ambiguous requirement, whether a design is coherent, or whether a spec is missing a subtle business rule—are judgment calls. An LLM can surface candidates, but it should report evidence and uncertainty rather than silently certify correctness.
From tests to runtime evidence
For critical non-functional requirements, tests are pre-production evidence—not the final proof. A requirement such as “API p95 latency SHALL remain below the agreed target” may need a benchmark, a rollout guardrail, and production telemetry. This connects SDD to SRE and governance: a specification is strongest when it has a measurable observation path after deployment.
A practical repository shape
project/
├── AGENTS.md
├── README.md
├── specs/
│   ├── constitution.md
│   ├── system/
│   │   ├── authentication.md
│   │   └── payments.md
│   └── changes/042-session-timeout/
│       ├── proposal.md
│       ├── requirements.md
│       ├── design.md
│       ├── tasks.md
│       ├── verification.md
│       └── decisions/
├── contracts/
│   ├── openapi.yaml
│   └── schemas/
├── src/
├── tests/
└── .github/
The exact folders do not matter as much as the lifecycle: durable principles are easy to find; current capability behavior is distinct from proposed change; implementation work is bounded; verification is preserved; and all of it moves through Git review with the code it governs.
Start small: an adoption sequence that will not stall delivery
- Choose one medium-risk, cross-cutting change where ambiguity or review cost is already visible.
- Create a short change spec with goal, non-goals, scenarios, constraints, and evidence requirements.
- Require repository evidence in the technical design; reject invented parallel abstractions.
- Break the work into small task contracts and preserve human approval for consequential decisions.
- Ask an independent reviewer—human, agent, or both—to report requirement coverage and missing evidence.
- Archive or update the spec after release, using operational evidence to correct what the team thought it knew.
- Only add heavier traceability or automation where the risk and coordination benefit justify it.
References and further reading
Primary tools and workflows
Spec Kit
GitHub Spec Kit documentation
Official documentation for Spec Kit’s core Spec → Plan → Tasks → Implement workflow, templates, and agent integrations.
Agentic SDD reference
Official reference for the richer constitution, specify, clarify, plan, checklist, tasks, analyze, implement, and converge workflow.
GitHub: Spec-driven development with AI
GitHub’s September 2025 explanation of its intent-first approach and the distinction between what to build and how to implement it.
OpenSpec and Kiro
OpenSpec: core concepts
Official overview of canonical specs, change folders, delta specifications, proposal/design/tasks, and archiving changes into current truth.
OpenSpec in existing projects
Official guidance on behavior-first delta specs for brownfield work without documenting an entire codebase first.
Kiro Feature Specs
Official Kiro documentation for requirements-first and design-first feature workflows, EARS notation, design, tasks, and review.
Evidence and adjacent practices
SWE-bench: Can Language Models Resolve Real-World GitHub Issues?
A repository-level benchmark illustrating that issue resolution involves long contexts, multi-file coordination, execution, and reasoning beyond isolated code generation.
Context Engineering for AI Agents in Open-Source Software
Early research on project-specific context, agent configuration files, and the emerging AGENTS.md convention; treat findings as evolving evidence.
Cucumber: Behaviour-Driven Development
Official explanation of BDD as shared understanding through concrete examples and continuously checked system behavior.
EARS and EARS+
Alistair Mavin’s structured requirements notation and its use for clearer, testable natural-language requirements.